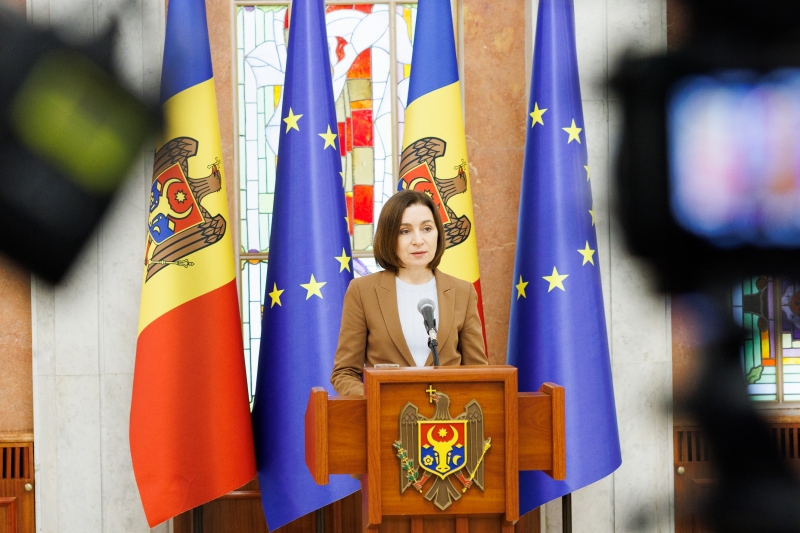
President Maia Sandu stated after the meeting of the National Security Council (NSC) that, in October 2026, the Republic of Moldova’s government systems were targeted by a massive cyberattack. The institutions summoned to today’s National Security Council meeting presented the findings of their investigations into the scale of the attack, the methods used by the attackers, the vulnerabilities exploited, the immediate measures taken during those days, as well as medium- and long-term systemic proposals aimed at strengthening the state’s cybersecurity and ensuring a higher level of protection for government digital services, TRIBUNA reports.
According to the head of state, the incident occurred within the infrastructure managed by the Electronic Governance Agency (AGE), affecting several services. The root cause was structural and related to governance, as the systems verified only the application requesting data, without checking the identity of the user or their authorization to access that data. As a result, a single application with flawed access controls exposed the registers of at least ten institutions.
The attacker, possessing a set of personal identification numbers (IDNPs), gained access to the system and extracted data, which was subsequently used to penetrate further into the infrastructure and obtain complete personal records. The incident was the consequence of an architecture in which data from all registers could be accessed through a single point, without oversight by the data holders or limits on the volume of information retrieved. There was also no automatic alert mechanism when a certain data extraction threshold was exceeded.
The institutions presented the following timeline of the attack: automated requests originating from more than 638 IP addresses, which concealed the actual source, began on the evening of October 19. The most intense activity occurred on October 20, when approximately one million requests were recorded in a single day, 30 times the normal average. On the same day, more than 260,000 records containing information about relatives were extracted.
On October 21, AGE stopped the exfiltration of data concerning relatives. By October 23, the process of blocking the attackers had begun. On October 24, all attacks were blocked, and the attackers were no longer able to steal data. Attempts continued afterward but were repeatedly blocked by the institutions.
“The communication of state institutions regarding the incident was delayed and did not address all the concerns of citizens. The absence of a communication protocol for such situations led to uncertainty regarding responsibilities and responses.
The latest assessments indicate that the data of approximately 450,000 citizens was accessed. This figure is lower than the numbers circulated in recent days, but it is still significant. These people will be notified by the Electronic Governance Agency,” the President stated.
Maia Sandu Also Explained What State Institutions Have Done So Far
The massive cyberattack has been stopped. AGE disconnected all electronic services and platforms integrated with MPass, and following the implementation of corrective measures, they were gradually restored.
Problems related to authentication and access control services have been resolved. Verification mechanisms now ensure that the entity requesting data is the legitimate data holder. Access points have been secured through mandatory authentication, while responses have been restricted to strictly necessary information.
Administrators of all systems integrated with MPass received instructions and an additional verification test, which was implemented urgently.
“What Citizens Need to Know”
“First of all, the cyberattack did not compromise the integrity of banking data. Even though IBAN details were extracted, this information alone is not sufficient to access your bank accounts. Nevertheless, banks will be informed about the individuals whose data was accessed so that additional checks can be carried out if transactions are initiated in their names.
The risk is that the extracted data could be used in combination. For example, an IDNP together with information about relatives or driving licence details, sometimes combined with an IBAN, could be used to contact people for fraudulent purposes. In other words, someone who has access to certain personal information about you may call or message you, pretending to represent a bank or the police, and request additional information.
Dear citizens, no state institution or bank requests PIN codes, passwords, or bank card details by phone or SMS. If you receive such a call, hang up and contact the bank or police directly using the telephone numbers published on their official websites, not the number from which you were called. It is better to refuse a call than to become a victim of fraud.
The Electronic Governance Agency has published telephone numbers and other contact details that citizens can use if they suspect an attempted fraud or need information about their personal data. For immediate assistance, call 112,” the President added.
Measures Agreed Upon at the National Security Council
The NSC agreed that state institutions, including the Ministry of Education, should prepare a model lesson for middle and high school students, explaining several basic rules for protecting personal data.
These include avoiding overly simple passwords or using the same password across multiple platforms, changing passwords periodically, enabling two-factor authentication for email, social media accounts, and other applications, and exercising greater caution when encountering suspicious links, free offers, and other potential online threats.
The authorities also expressed hope that young people would subsequently help their parents become more vigilant and better protected.
In addition, the National Cybersecurity Management Center (CNMC), in cooperation with the Cybersecurity Agency, will prepare a simple personal data protection guide, providing clearly explained steps for all citizens.
“Our cybersecurity depends both on the state’s ability to secure its infrastructure and on each individual’s ability to protect their own data.
There may also be another risk: people could temporarily lose access to certain services due to platform failures or preventive shutdowns.
One of the most serious consequences is, in fact, the weakening of public confidence in the state’s cybersecurity and the safety of digital services. This is precisely where the responsible state institutions must act immediately and sustainably,” she emphasized.
Maia Sandu Also Outlined the Next Steps for State Institutions
The theft of data has been stopped, but institutions must continuously adapt to reduce the risk of similar attacks in the future.
The most important changes involve restricting access to data without authentication, conducting security testing of all services, and redesigning the infrastructure to ensure a unified and secure digital architecture.
Another issue that needs to be addressed is the fragmentation of responsibilities among government institutions, which delayed the detection of the problem and, consequently, the coordination of the response to the incident.
“Today, at the National Security Council, we discussed numerous solutions — short-term measures to address the recently identified problem, but especially medium- and long-term solutions, because it is clear that in the age of artificial intelligence, these risks will increase.
We agreed that a working group will be established under the leadership of the Prime Minister. Within one month, this working group will propose systemic solutions to cybersecurity issues in the Republic of Moldova. In three months, we will meet again at the National Security Council to monitor the progress achieved during this period.
We discussed addressing the architectural problems because, as I mentioned earlier, the incident revealed a serious flaw in the system’s architecture.
The system is outdated, and this must also be acknowledged. We need to establish expiration dates for information systems. We are pleased when a new system is launched, but sometimes institutions forget to determine its operational lifespan and expiration date. A new system is needed — one that will resolve the architectural problems of the existing infrastructure.
We also discussed the need to reform the procurement system in the field of information technology. In this regard, the procurement process must be made more secure.
We discussed the need to establish and implement clear rules covering the entire lifecycle of information systems, including all stages of testing, operation, and maintenance. These measures must ensure that information systems remain secure over time and are replaced when they can no longer guarantee adequate security.
Regarding governance, the problem was detected too late, and once it was identified, the response of the institutions was insufficiently coordinated. The Government has undertaken to develop a proposal to clearly define the responsibilities of institutions, avoiding overlapping mandates while ensuring rapid and effective interinstitutional cooperation.
The technical details of several decisions cannot be made public for security reasons, in order to prevent them from reaching malicious actors,” the President of the Republic of Moldova concluded.



 Loading ...